Know about the attack
before it happens
Silent Push maps adversary infrastructure while it is still being built and turns it into Indicators of Future Attack® (IOFA), so your team can act before a campaign is ever launched.
What is preemptive cyber defense?
Preemptive cyber defense finds adversary infrastructure during the setup and staging phase before an attack is launched. It shifts detection to the preparation phase, when adversaries are registering domains and standing up hosting, so teams get the lead time to block a campaign before it goes live.
Most of an attack is preparation in plain sight. Silent Push tracks every change across that whole phase, giving you complete visibility and months of lead time before the attack lands.
How does Silent Push do this?
Silent Push's Context Graph maps the internet's DNA. It continuously analyzes benign, gray, and malicious infrastructure to detect the management patterns adversaries repeat when they build and rotate their infrastructure. Future threats emerge from infrastructure that looks benign today, so it measures all of it, tracking DNS relationships, infrastructure changes, and content changes to expose adversary staging grounds as they appear.
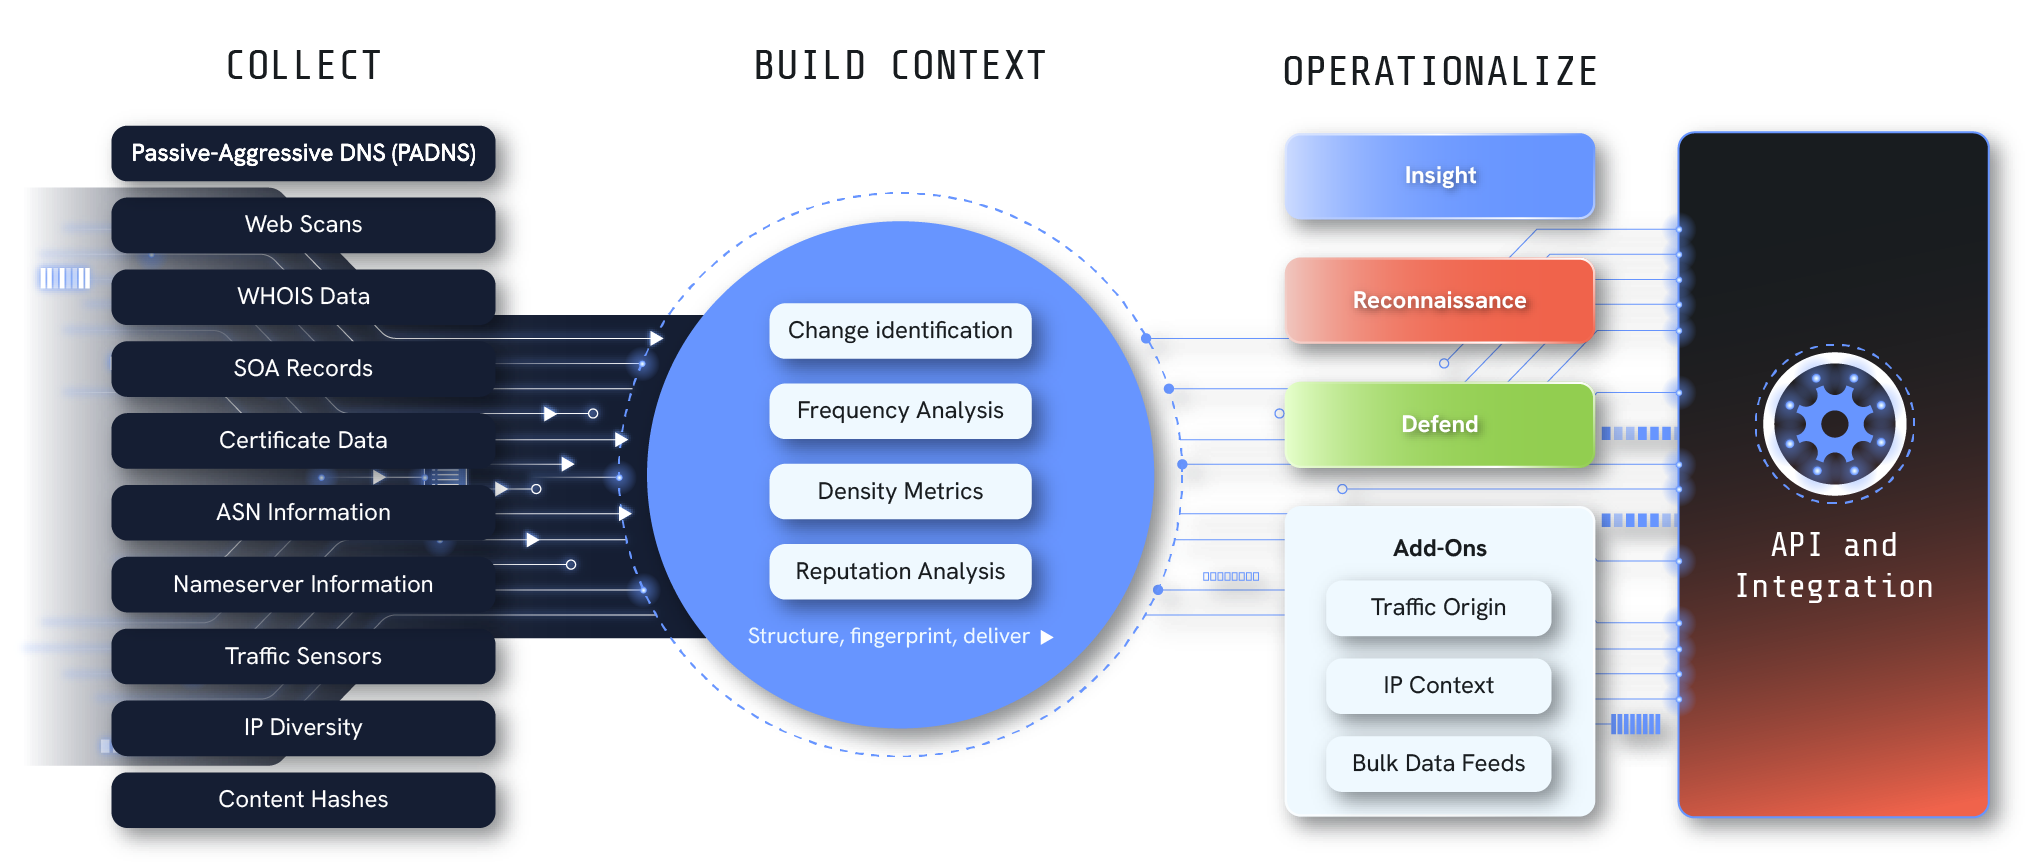
Passive-Aggressive DNS (PADNS)
A proprietary collection process that forces daily resolution of domains and IPs, detecting change before any traffic occurs.
WHOIS & Zone Files
Monitors ownership and registration changes in real time as new infrastructure appears.
Host Scans & SSL
Fingerprints server configurations across the internet to catch the signatures attackers reuse.
Honeypot Data
Captures direct interaction from adversarial scanning and reconnaissance.
Traffic Sensors
Attribute proxy and VPN traffic to its true country of origin, exposing adversaries hiding behind residential networks.
Behavioral Fingerprinting
Measures density, diversity, and rate of change to cluster infrastructure to the actor managing it.
IOFA identify adversary infrastructure during the setup and staging phases, before an attack is launched. They flag the domains, IPs, and hosting attackers are building while there is still time to block them.
The signals are grounded in observed infrastructure behavior across DNS, hosting, and content, so your team acts on verified facts and blocks campaigns weeks or months before weaponization.
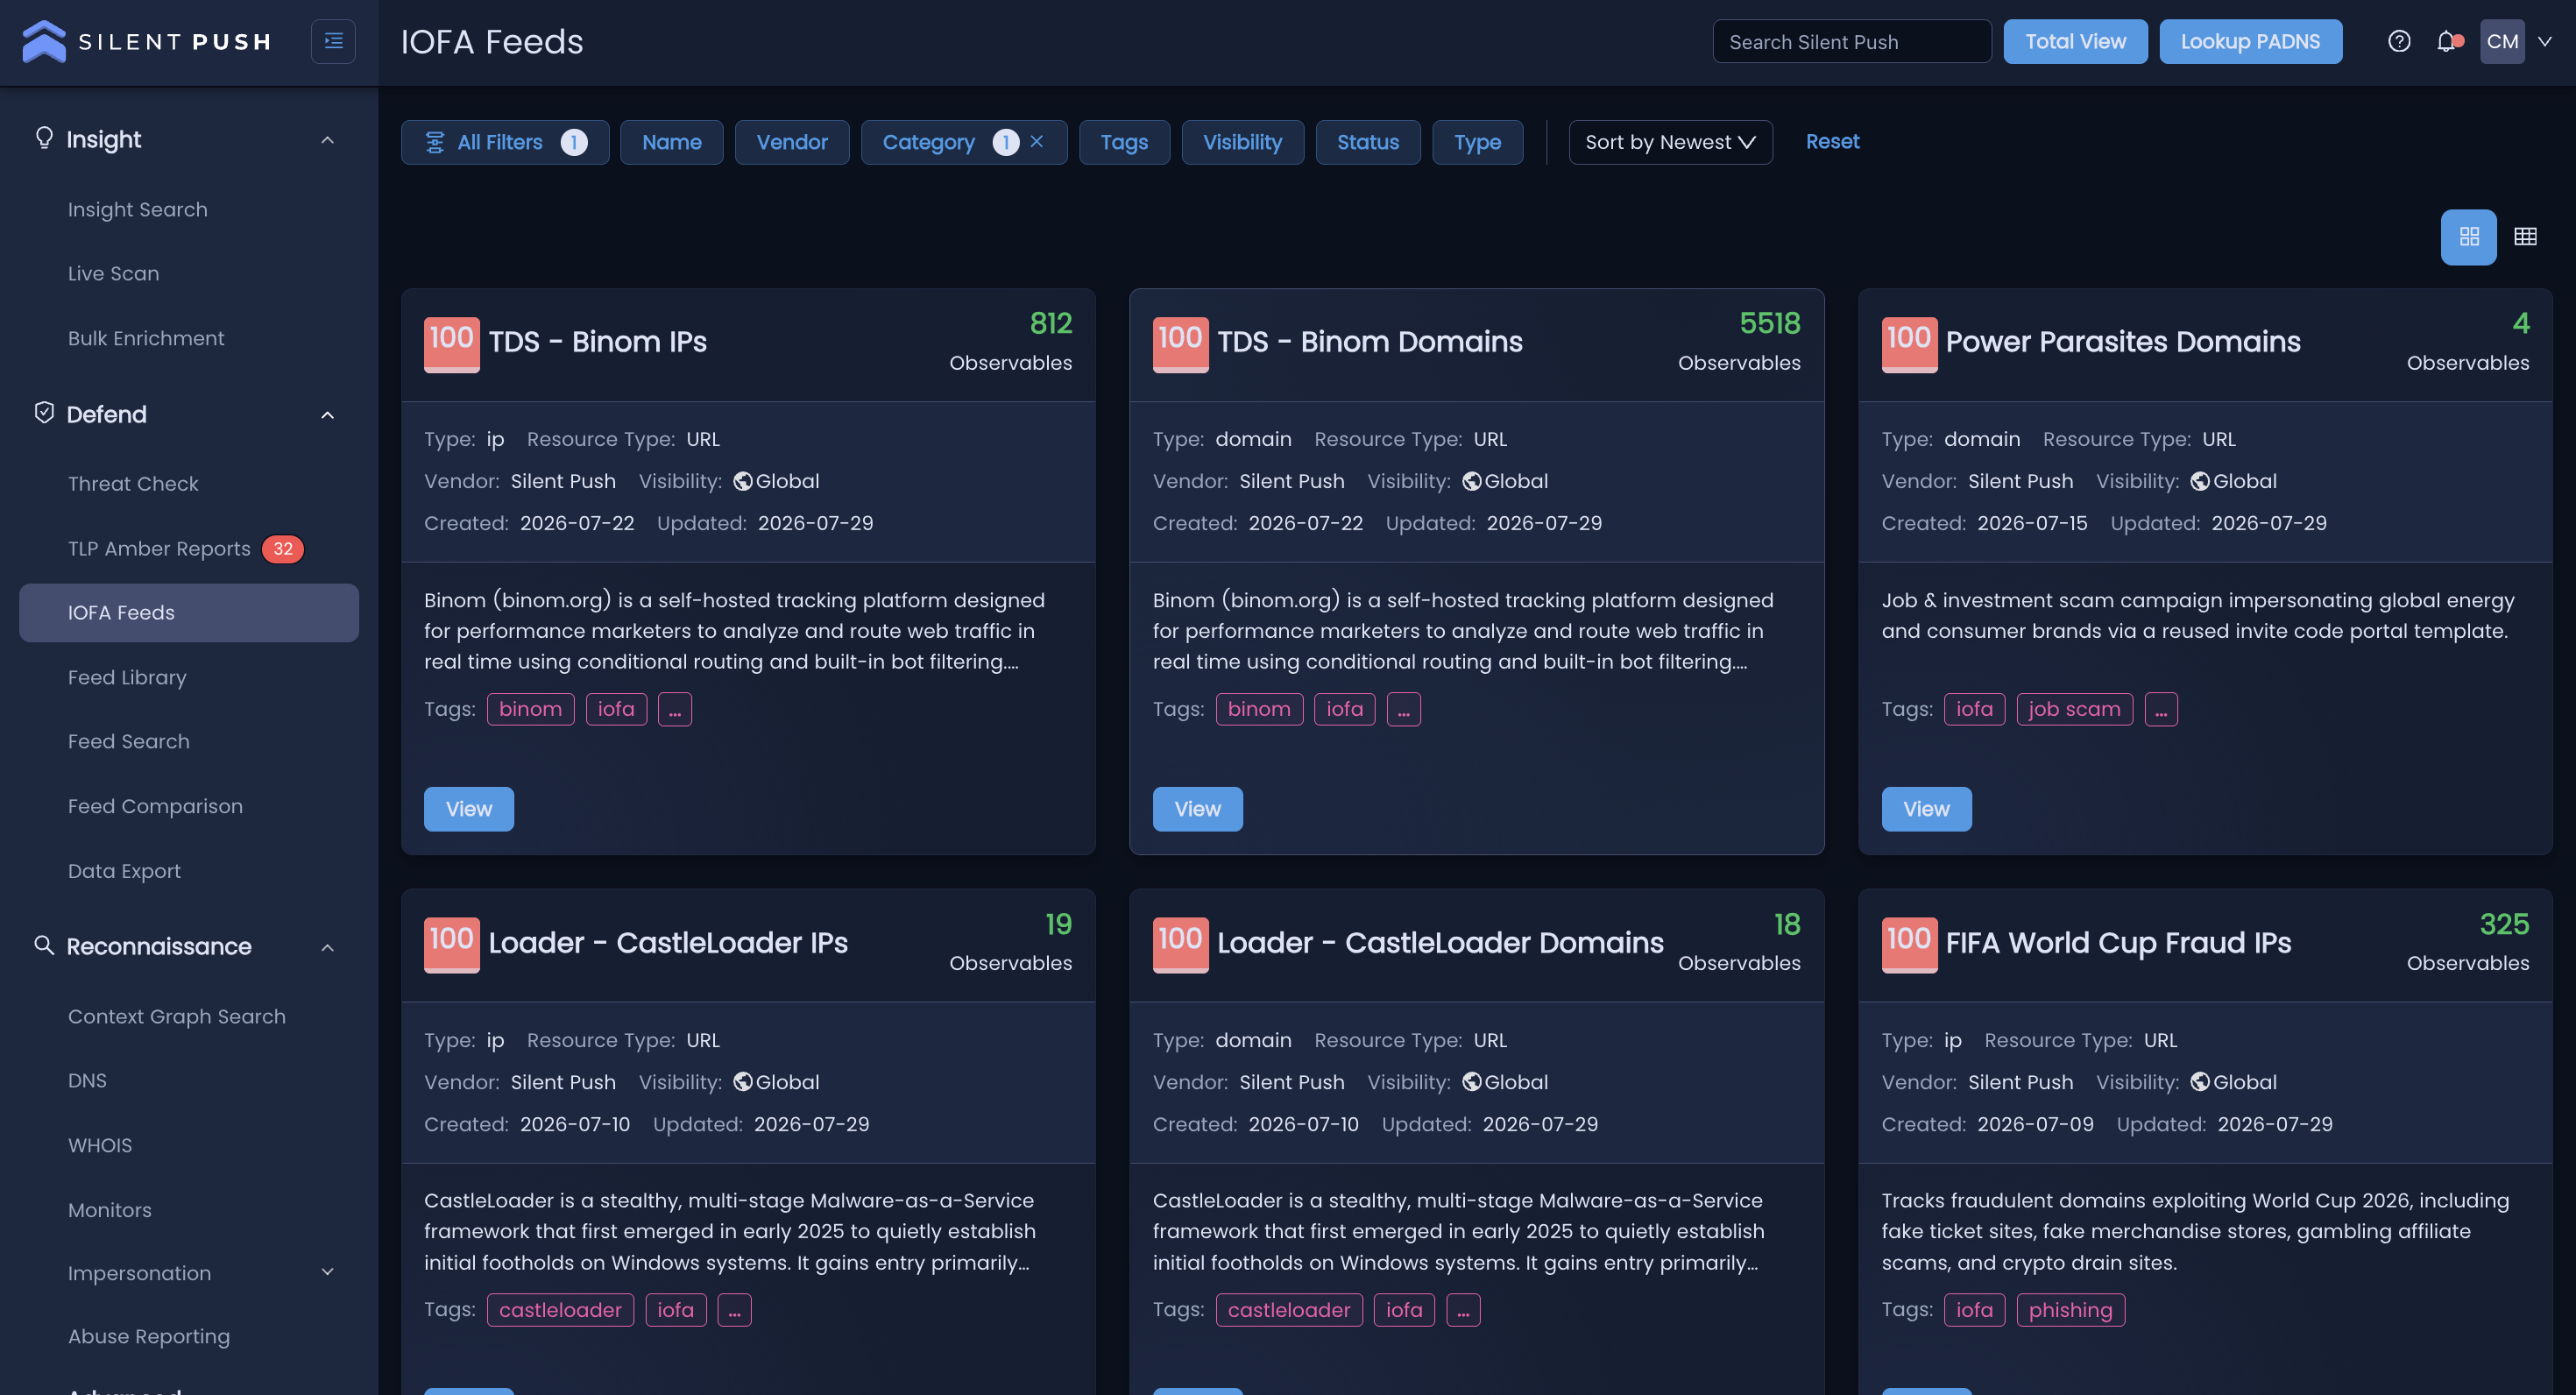
Three modules, one workflow
Insight
See everything in one place about any domain or IP, and accelerate triage with 70 to 100+ contextual attributes and proprietary Risk Scores.
Reconnaissance
Pivot out to find more of the same infrastructure and map adversary campaigns during setup and staging, before weaponization.
Defend
Operationalize findings into SIEM, SOAR, firewall, and TIP workflows, and build your own feeds for automated blocking.

Built to work inside your stack
Silent Push is API-first and additive. It sits alongside the tools you already run and fills the gap they leave: infrastructure-level visibility in the weeks before an attack is deployed. Nothing to rip out, nothing to rebuild.
API-First
200+ endpoints push IOFA feeds, reputation scoring, and SPQL queries into your existing pipelines.
MCP Server
Query the intelligence in plain language inside Claude, Cursor, and other MCP-compatible tools.
SIEM, SOAR & TIP
Enrich and block automatically inside the platforms your team already runs.
Agentic Workflows
Machine-consumable data grounded in observed infrastructure gives agentic workflows a source of truth they can act on.