
- Company
Silent Push Inc. ©2025
Last week, we were at the Moscone Center in San Francisco for the world’s largest cybersecurity event, RSA, along with 45,000 professionals from across the globe, to explore emerging threats, share innovations, and shape the future of digital defense.
Our conversations with CISOs, industry leaders, threat analysts, and security architects, expressed a growing need for earlier visibility into adversary infrastructure.
RSAC 2025 featured the latest trends in threat intelligence, AI-driven security, and proactive defense strategies.
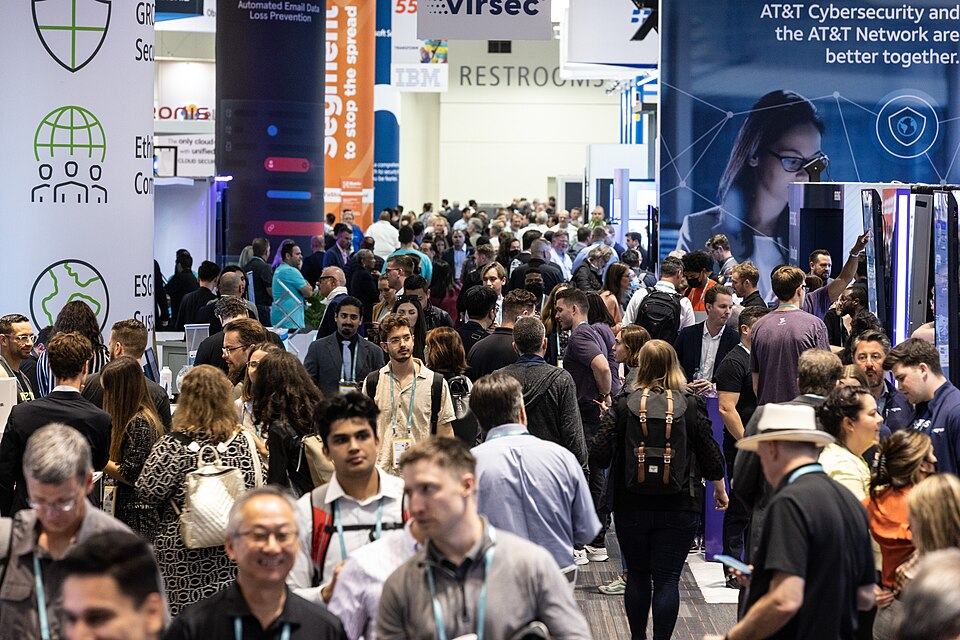
Following our company announcement outlining significant updates to our Threat Intelligence module, our executives met with journalists from the Wall Street Journal, CSO Magazine, and ChannelE2E/MSSP Alert to discuss the cybercrime landscape, our work with the World Economic Forum Cybercrime Atlas Group, and the challenges organizations face to locate and block malicious infrastructure as it’s being set up.
Read about our RSA media coverage in various outlets:
Held at City View at the Metreon in San Francisco, this year’s BSides was themed “Here Be Dragons” – a perfect fit for the kinds of tough, uncharted challenges security teams are facing right now.
Our Senior Threat Analyst, Zach Edwards, gave a talk titled “A Deep Dive into the Triad Nexus Pig Butchering & Money Laundering Network.” He demonstrated how Silent Push helps security teams spot the infrastructure behind major fraud operations as it’s being built, giving defenders a much earlier shot at stopping attacks.
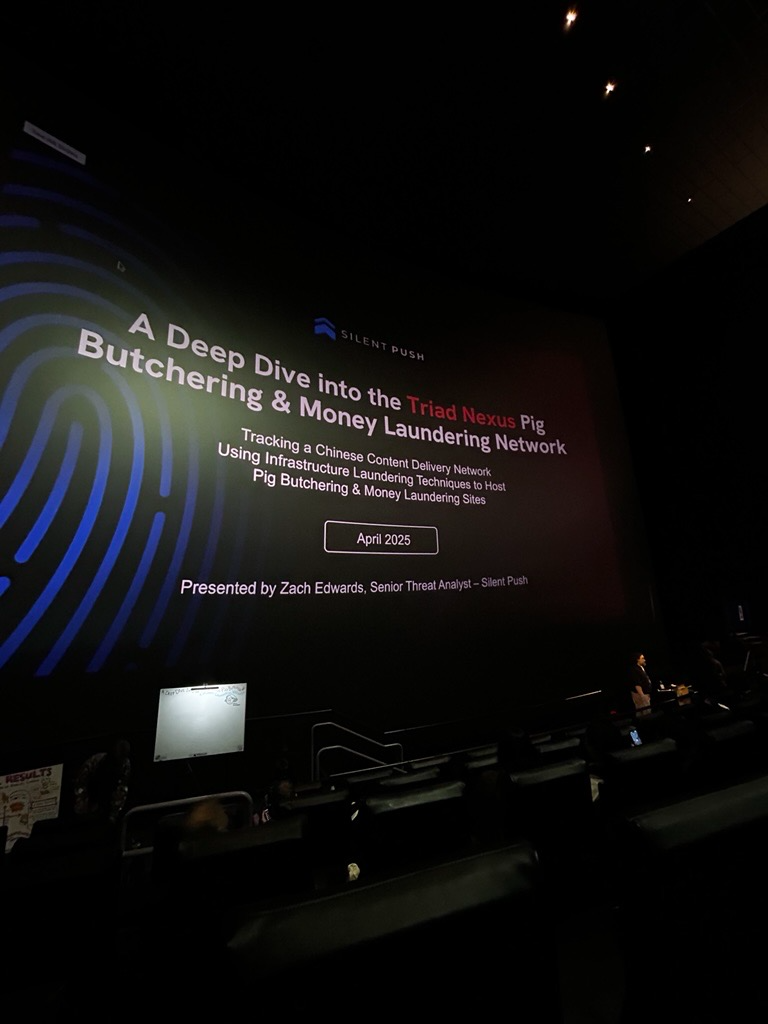
Read Zach’s research here.
It was awesome to connect with so many red teamers, blue teamers, and threat researchers throughout the weekend. The conversations we had highlighted how critical it is to move faster and detect bad infrastructure before it’s fully operational.
We were at the Mercure MOA Hotel Berlin, for FIRST Berlin. Our Chief Revenue Officer, David Troha, delivered a welcome speech, setting the tone for three days of technical discussions and community building.
As a premier gathering of global incident response and threat intelligence professionals, the event promotes collaboration, innovation, and the sharing of best practices to strengthen the cybersecurity community’s ability to detect and stop threats.
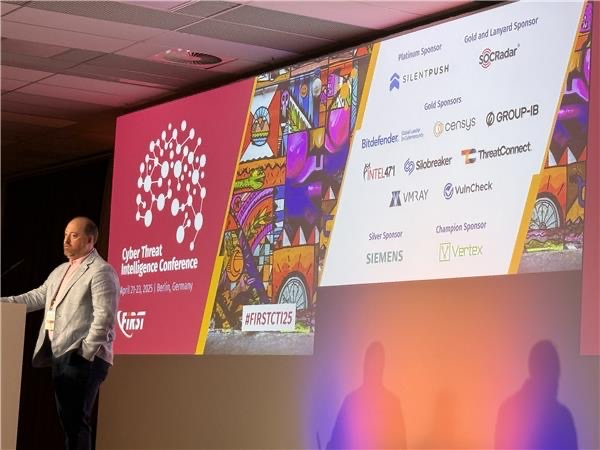
David emphasized the growing importance of early detection and the critical role of infrastructure intelligence in staying ahead of increasingly sophisticated adversaries, which is central to what we’re trying to achieve at Silent Push.
Throughout the event, our conversations with CSIRTs, PSIRTs, and intelligence teams reinforced the urgency of proactive threat detection.
SANS Nationals is the SANS Institute’s flagship cybersecurity training and networking event, that aims to build stronger, more resilient security teams.
During the event in Orlando, our Threat Analyst João Ferreira gave a well-attended seminar on “Advanced Techniques for Detecting New Malicious Infrastructure”, which showcased how Silent Push empowers security teams to proactively identify adversary infrastructure at the earliest stages – as it is being deployed, not after an attack has already occurred.
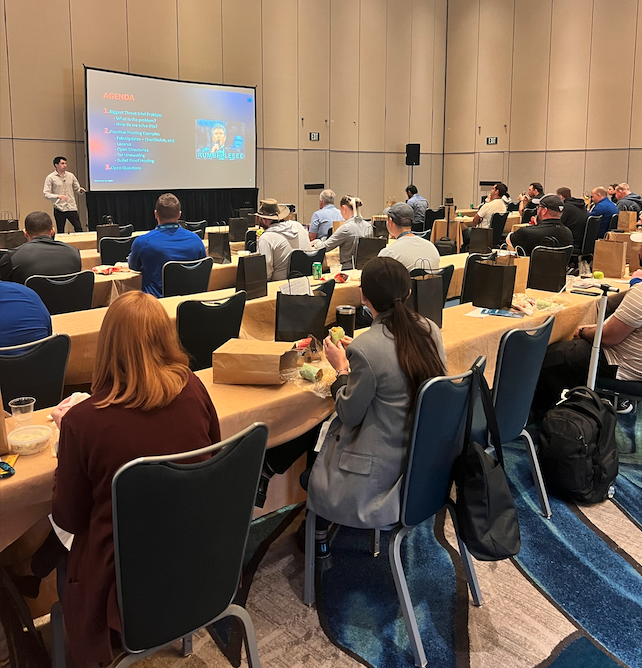
Our platform’s ability to map and detect emerging threat infrastructure resonated strongly with attendees. Conversations with security engineers, threat hunters, and SOC leaders revealed a growing demand for solutions that move beyond reactive detection.
Engaging with the SANS community provided us with valuable feedback on how organizations are evolving their security postures, and reinforced the critical need for TTP-led detection strategies.
We started off the month at the National Cyber Security Show 2025, which took place at the National Exhibition Centre (NEC) in Birmingham, UK.
The event brought together cybersecurity professionals, industry leaders, and technology innovators to explore the latest solutions, trends, and strategies in cybersecurity.
Our CEO, Ken Bagnall, delivered a keynote speech on “Finding Adversary Infrastructure before the attack: Future-based threat intelligence”.
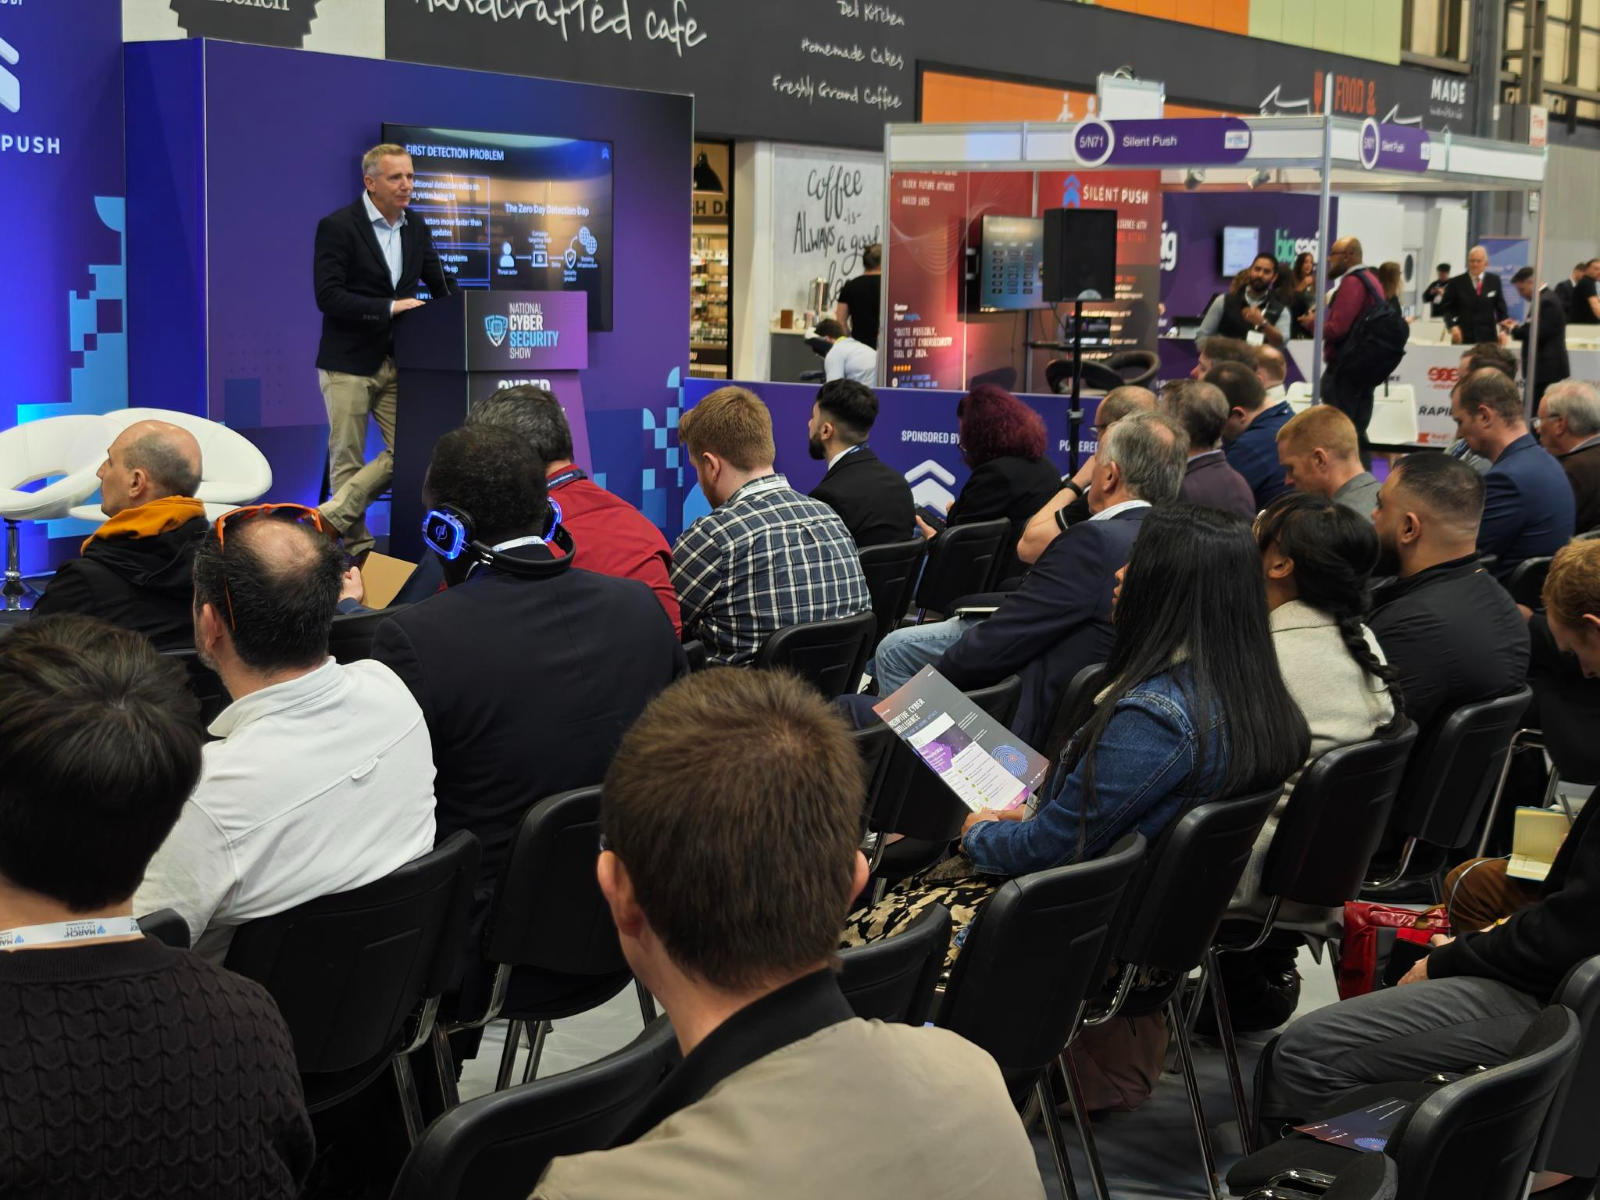
Our team had the opportunity to network, participate in insightful seminars, and discuss cutting-edge technologies, such as our own platform, that are designed to protect UK businesses and individuals from evolving cyber threats.
The Silent Push team will be at the Health-ISAC 2025 Spring Americas Summit, from May 19 -23 at the Naples Grande Beach Resort in Naples, Florida.
Themed around “Creating Safe Harbors”, the summit serves as the premier gathering for healthcare cybersecurity professionals, focusing on enhancing the security and resilience of the healthcare sector.
Stop by Booth 49 to see the Silent Push platform in action, with our Chief Revenue Officer, David Troha, and Director of Sales Engineering, Maulik Limbachiya.
Join our community and start revealing unknown threats today. Get in touch here to schedule a meeting.
Silent Push Threat Analysts discovered an X/Twitter post on May 1, 2025, promoting the non-existent product, “Apple iToken.” The advertising display URL showed “From CNN[.]com,” which appeared to be done via a known exploit for spoofing a URL on X/Twitter.

This campaign is abusing a known loophole in X/Twitter display URLs. In March 2024, Bleeping Computer reported on a similar cryptocurrency scam that spoofed the forbes[.]com domain on X/Twitter.
The simplest way to explain how this is done is that the exploit is possible on X/Twitter because of a few features:
A similar version of this spoofing effort can be done using URL shorteners, as in this current live example. The threat actors merely set up the URL shortener to initially redirect people to a benign website like CNN[.]com. After submitting the URL to Twitter and posting the card with the CNN metadata, they then updated the URL shortener with a new URL so that it sends everyone else to the new destination.
After the final X/Twitter redirect, the visitor is taken to ipresale[.]world, which features the previously mentioned classic cryptocurrency “presale scam,” encouraging them to navigate the process of creating an account and buy an “iToken” that’s positioned as coming from Apple.
Register now for our free Community Edition to use all the tools and queries highlighted in this blog.
The initial X/Twitter ad appeared to come “From CNN[.]com.” However, if one clicks on the ad, the chain actually goes through the following URLs:
The first Bitly URL was created on May 1, 2025, at 19:22 UTC – likely right before the ad launched on X/Twitter:
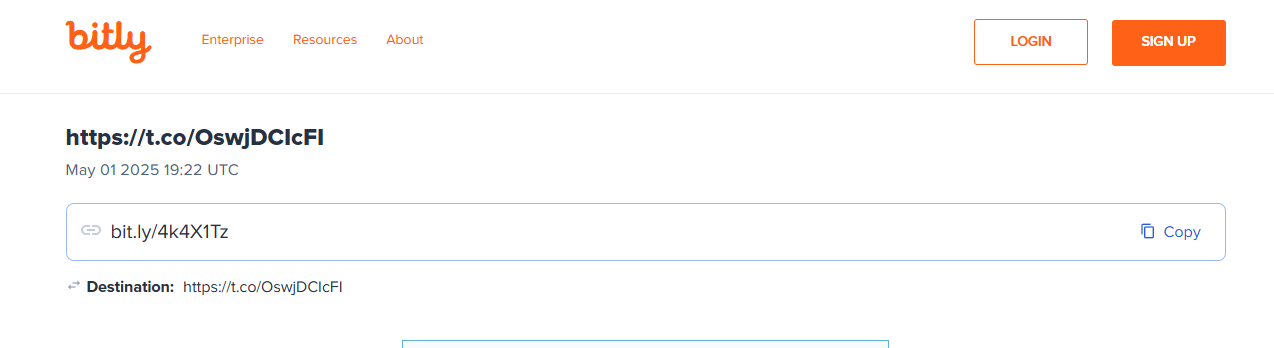
The Bitly URL redirects to an X/Twitter URL-shortened link, t[.]co/OswjDCIcFI, essentially returning the user to Twitter before redirecting to the final domain in the scheme.
It appeared that the original user who paid for and posted the X/Twitter ad posted a separate tweet linking to this domain and then copied the X/Twitter tracking URL to embed into the Bitly redirect flow.
After the final X/Twitter redirect, the visitor was taken to ipresale[.]world, which featured a classic crypto “presale scam.” The website spoofing Apple and a fake “iToken” product even includes a phony endorsement from Apple CEO Tim Cook during the crypto scam sales completion step.

If you click on the “Buy Now” link, you’re taken to a “/register” page that further features (and abuses) the Apple brand:

We tested the account creation process, and once we logged in, the interface looked like this:

Here is a short video that shows the process to buy an “iToken” via Bitcoin:
There were 22 wallet options for sending money into this scam. Since we found the scam site early after it was launched, there were no transactions at the time of our initial checks on the wallets:
After initiating the process to send a payment into one of the wallets, a “Waiting for Payment” interstitial is loaded:
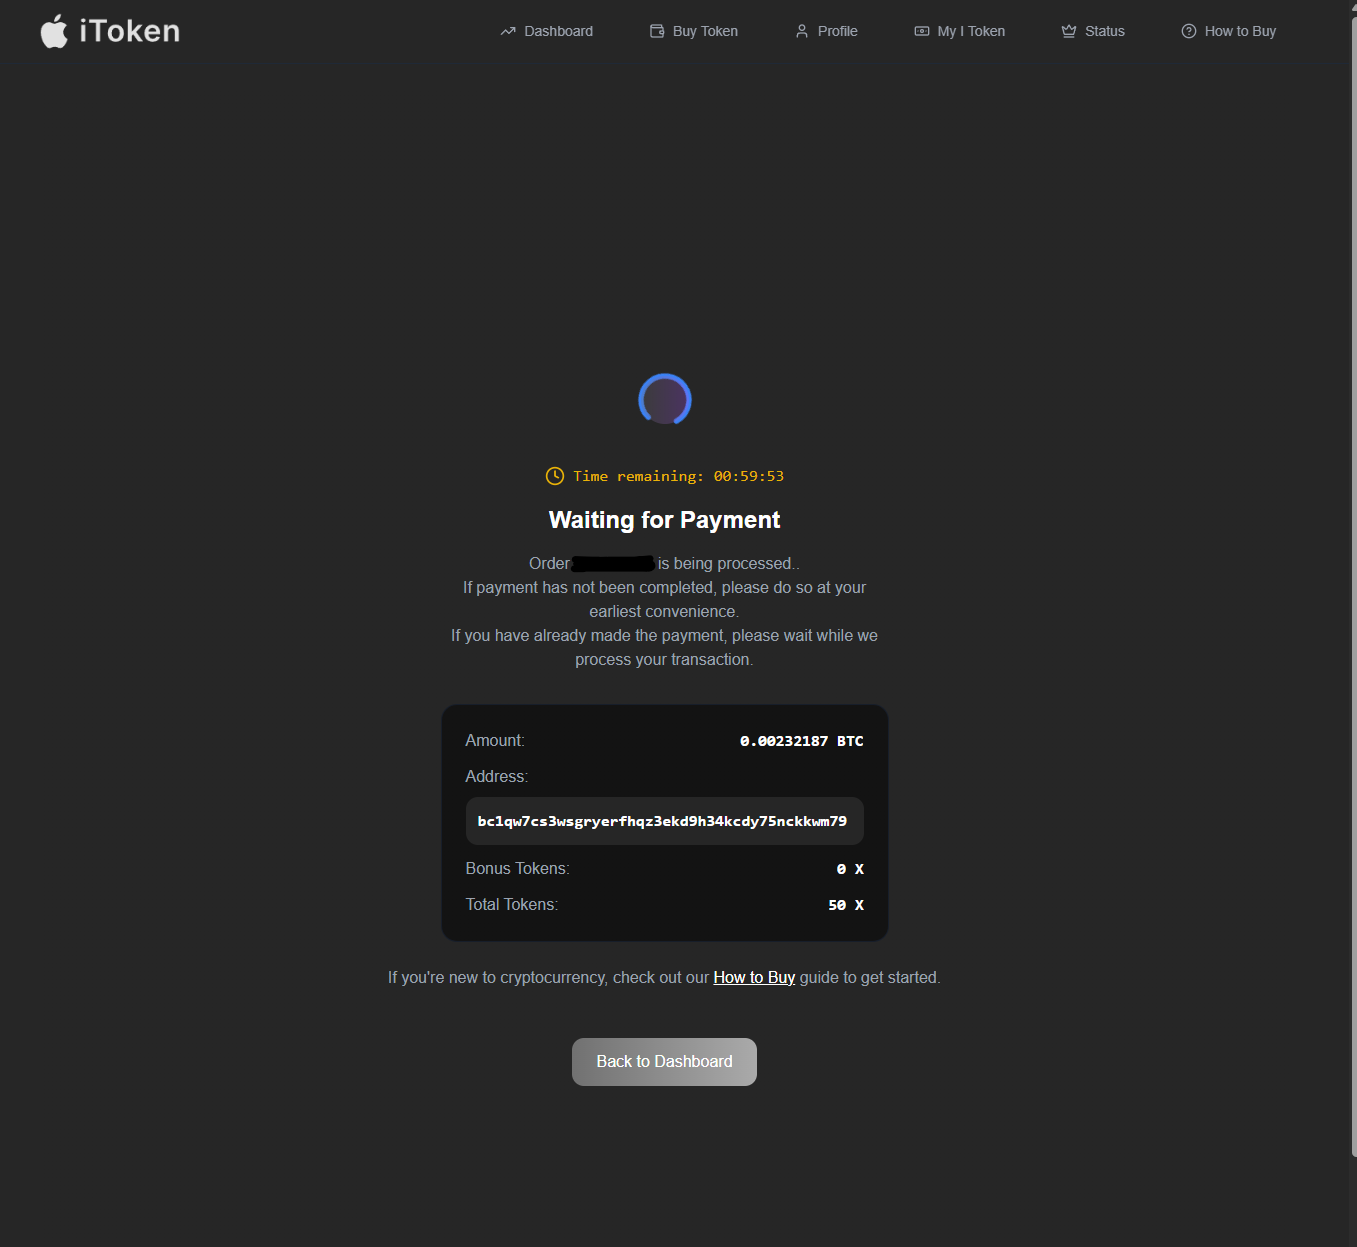
If you try to access the URL without a working orderID, the page gives an error:

If you click “Back to Dashboard,” you will see details about any transfers and a fake quote from Apple CEO Tim Cook.

The phony Cook quote reads, “Excited for the future of blockchain with I Coin. Stage 3 presale is live at $4.5—next stop, $27.50. Secure, transparent, and built for the decentralized world ahead. Now’s the time. #ICoin #BlockchainFuture”

Other pages on the site included a “My Profile” page:

The “My Token” page that follows would likely be populated with details if a funds transfer was successful. At the bottom of the page, “Recent Activity” included pending transactions:

There was also a “Status Tiers” page – essentially a purchase loyalty program that the threat actor was promoting, which featured tiers for: Bronze, Silver, Gold, Platinum, Diamond, and Legendary.
Finally, there was a “How to Buy” page with additional instructions for purchasing tokens via crypto wallets or exchanges:

On May 5, 2025, Silent Push Threat Analysts picked up another X/Twitter ad from this campaign using the bit[.]ly domain shortener domain instead of a more prominent domain like cnn[.]com.
The tweet can be found here. It redirects through a third domain via a redirect flow like this:
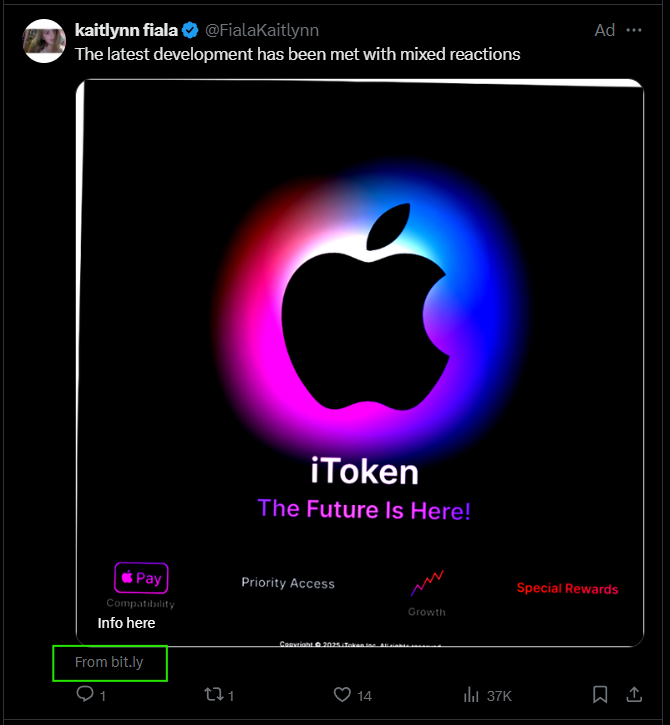

The “iToken” website (itokensale[.]live/landing) shown after the redirects was nearly identical to the first site that we found.

So, why cover this particular threat?
Because the domains found in pivots above, including ipresale[.]world, are a perfect use case for our new Silent Push “Web Resource Scan” data source, which provides essentially all the files that load on any scanned webpage, from HTML and CSS to images and JavaScript and everything in between.
We started this investigation by searching our new data source for the suspicious domain to expose all the files seen on that domain.
Web Scanner domain search query link

Analyzing the data our Web Resources Scan returned for the domain, we found a few different unique files were being reused across a grouping of similar domains:
The overlapping queries returned unique domains, all hosted on Hetzner (ASN24940):
The other site that was live within the network looked identical to the first:

We can conduct a similar search for Web Resources Scan data from the domain we found used in the most recent X/Twitter ad campaign, itokensale[.]live. This resulted in the discovery of a similar CSS file and a SHA256 hash of that CSS file, which can be used to pivot into even more domains.
We started with a broad search for all files found in the Web Resources Scan data source for the itokensale[.]live domain.
Web Scanner Domain search query link
And if we grab the SHA256 for the “index-DIX1ewrp.css” file found above, we find it’s another solid pivot into more of these sites:
Web Scanner SHA256 search query link
The query above returned seven domains, all matching the previously-seen patterns:
The most recent campaign included a redirect from chopinkos[.]digital to itokensale[.]live.
Investigating chopinkos[.]digital, we found that the domain was registered on May 5, 2025, on PublicDomainRegistry[.]com (PDR) and immediately weaponized.
The Silent Push Web Scanner picked up content from the newly registered domain, which included the HTML title “iToken,” hosted on Cloudflare (ASN13335) with the path “/landing”
These fingerprints can be searched to find even more of the domains used by this campaign, including some that look like this interstitial redirect domain.
Web Scanner HTML title + geoip.asn + path query link
The query above returned a few domains found via previous fingerprints, as well as some new ones:
The previously seen domain, isale[.]ltd, was registered on PDR on April 28, 2025, and mapped to an IP address on Hetzner the next day.
The NameServer records are for “ns1.chsw.host” + “ns2.chsw.host” – this “chsw.host” NS record is only used by 268 hosts, and many of its domains are suspect .ru sites, while others appeared to be financial scams.
After a review, it appears to be safe to block, or at least alert on, domains using this NameServer:
Silent Push Explore Indicator DNS Data search query link

But within all the sites that used this NameServer were results from the previous file searches, along with a series of other domains that were live in 2024 and 2025 that appeared to target X/Twitter users with financial scams, as well as many that appeared to abuse Apple trademarks:
Across the previous pivots and domains found, four favicons were being reused within the campaign – three impersonate Apple and one impersonates X/Twitter:
These favicons are unique and exclusively used by this threat actor group. Knowing that, we could easily find even more of their sites with a simple query:
Web Scanner Favicon search query link
This query returned 82 results, including some overlap from the previous queries, some dedicated IPs used, and some “random-looking domains” that appear to have been used for URL redirections (like the previously found “chopinkos[.]digital”).
Many of the domains that used the previous NameServer, including the X/Twitter/Apple crypto investment scam websites, were also mapped to a specific IP address:
51.15.17[.]214 hosted on ASN 12876 “Online SAS, FR”, which can be seen in our platform here:
https://explore.silentpush.com/explore-result?name=51.15.17.214&queryType=query&type=ANYIPV4
While it’s no surprise that there are financial scams on X/Twitter, especially those that impersonate major brands, this most recent campaign’s ability to spoof the visible X advertising URL is a novel method for tricking potential victims, one only occasionally seen in the wild.
Given what our team uncovered during its research, the threat actor group behind this most recent X/Twitter advertising exploit is likely also behind many other similar domains and schemes.
This group also appears to have connections to numerous “.ru” domains. Although this can indicate ties to Russia, we have low confidence in that assessment. We will continue to track this campaign and share our findings as we learn more.
Silent Push believes all domains related to this financial scam on X/Twitter offer some level of risk to individuals and organizations. We provide client-only Indicators Of Future AttackTM (IOFATM) feeds for tracking malicious threats’ and APT groups’ associated domains and IPs.
Silent Push IOFATM Feeds are available as part of an Enterprise subscription. Enterprise users can ingest IOFATM Feed data into their security stack to inform their detection protocols or use it to pivot across attacker infrastructure using the Silent Push Console and Feed Analytics screen.
Silent Push is sharing an IOFATM list we have associated with the new crypto scam abusing Apple and X/Twitter to support ongoing efforts within the community.